If this resonated
Other pieces on PUBlish on the same threads.
AI
 Simon Ram#shopify
Two minutes, one incognito window
If you run a Shopify store, do this today. Open a new incognito window, add something to the cart, click checkout. Look at the address bar. …
Sign up to read →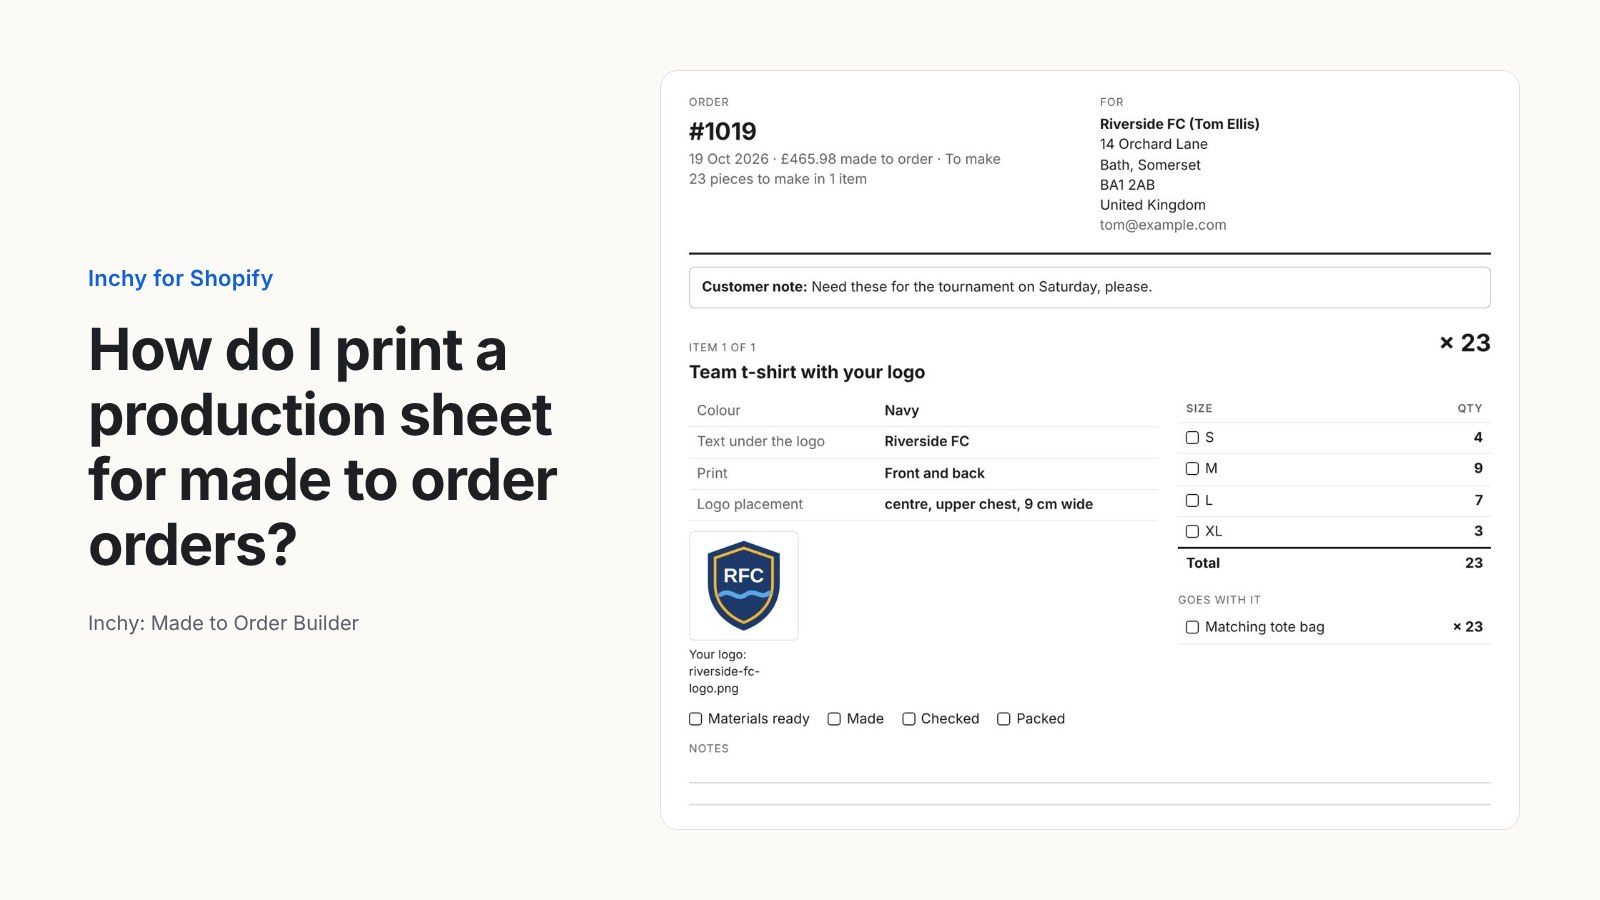 AI
 Inchy: Made to Order Builder for Shopify#shopify
How do I print a production sheet for made to order Shopify orders?
A made to order sale is only half done when the payment comes in: the sizes and choices typed on the product page still have to reach the pe…
Sign up to read →AI
 LeCon Wrat#ecommerce
Let them see the jacket first
The worst second in most online stores is the first one. You click an ad. The store opens. And before you see ONE product, a big box jumps i…
Sign up to read →AI
EEdd IT#securityWhose name is your domain in?
Quick question. If your website disappeared tomorrow, do you know whose name the domain is registered in? A lot of small businesses don't. T…
Sign up to read →